LLMsai
Google Suspends Open Source Vulnerability Rewards Amidst AI-Generated Noise
Google pauses its open-source bug bounty program until 2027 to address a surge in low-quality, AI-generated vulnerability reports.
4 min read
Google pauses its open-source bug bounty program until 2027 to address a surge in low-quality, AI-generated vulnerability reports.
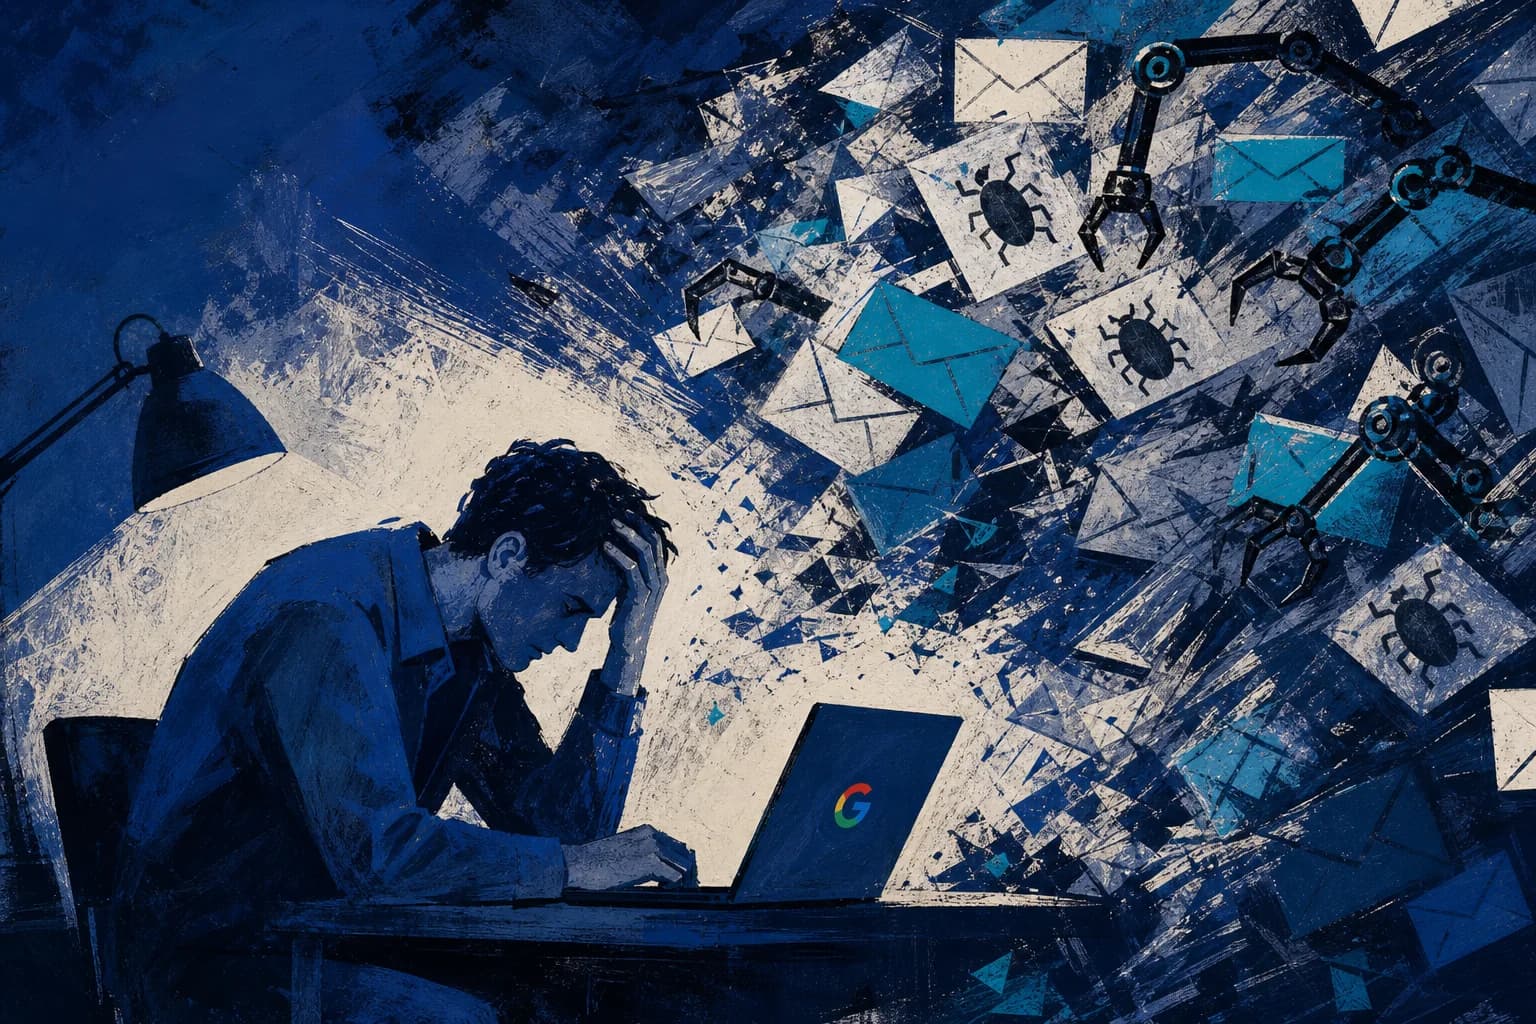
Google has officially suspended submissions to its Open Source Software Vulnerability Rewards Program, citing an unsustainable influx of low-quality, AI-generated reports that have compromised the efficiency of its security operations. This operational freeze, which is scheduled to remain in effect until at least the first quarter of 2027, marks a significant shift in how major technology firms manage external security research in an era of automated exploit discovery.
The decision follows a period where engineering teams and open-source maintainers reported being overwhelmed by thousands of invalid submissions. These reports, often generated by large language models and automated scripts, frequently contained hallucinated code flaws rather than verifiable security vulnerabilities. The sheer volume of this data has diverted essential resources away from addressing genuine threats within critical projects such as Golang, Angular, and Fuchsia.
Google clarified that the suspension specifically targets product vulnerability submissions within the open-source program. The company continues to accept supply chain reports and is maintaining its Google Patch Rewards Program, which incentivizes developers to provide verified code fixes. This program offers financial rewards of up to $15,000 for high-impact patches that address actual security weaknesses.
The broader ecosystem of open-source maintenance is experiencing similar pressures as the barrier to entry for vulnerability reporting has effectively vanished. Automated tools have enabled researchers to flood bug bounty platforms with reports that lack the rigorous verification required for meaningful remediation. This trend has forced maintainers to spend more time filtering noise than performing actual security auditing or code improvement.
Industry peers are encountering identical challenges, leading to a re-evaluation of traditional bug bounty models. The maintainers of the curl command-line utility recently terminated their HackerOne program due to the same deluge of automated submissions. Similarly, the Linux kernel community has struggled with a surge of bogus automated CVE reports that threaten to destabilize standard security triage workflows.
Intel also adjusted its security reward structure earlier this fall by removing financial incentives from certain bug bounty categories. These collective actions reflect a growing consensus among security teams that the current incentive structures for vulnerability reporting are being exploited by automated systems. The shift away from broad bounty programs suggests that organizations are prioritizing high-fidelity, human-verified reports over volume-based submissions.
The reliance on automated agents for security research has created a paradox where the tools intended to improve software robustness are instead creating systemic bottlenecks. By automating the generation of potential exploit paths, these models have outpaced the capacity of human maintainers to validate the underlying claims. This mismatch underscores a critical need for new verification protocols that can distinguish between machine-generated noise and legitimate security research.
Security teams must now determine how to integrate automated research without sacrificing the quality of their threat intelligence. The current triage workflow is failing because it lacks a secondary layer of automated verification that can cross-reference reported flaws against known code execution paths. Without such a mechanism, maintainers are forced to manually inspect every submission, which is an inherently non-scalable process in a high-volume environment.
The pause in the Google program serves as a necessary intervention to allow for a total reformat of the submission process. Future iterations of the program will likely require more stringent validation metrics to ensure that researchers provide actionable data rather than speculative code analysis. This transition is essential for maintaining the integrity of the open-source supply chain as automated discovery tools become increasingly sophisticated.
The coming months will likely see a move toward more exclusive, invitation-based research models or the implementation of advanced filtering algorithms designed to detect and discard machine-generated submissions. These developments will define the next phase of vulnerability management in the context of increasingly automated software development environments.